Security Operations Center (SOC) Services

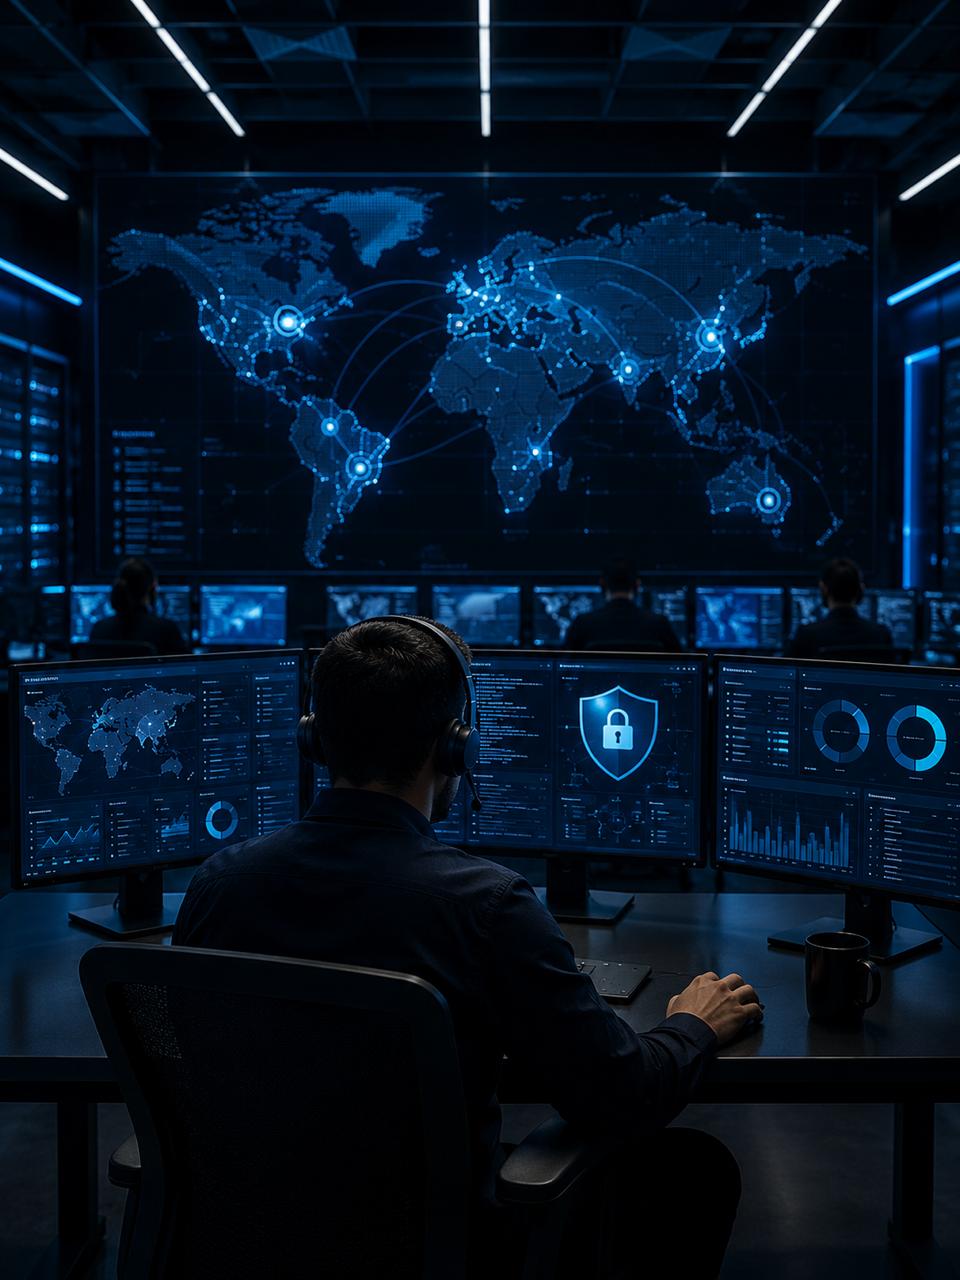
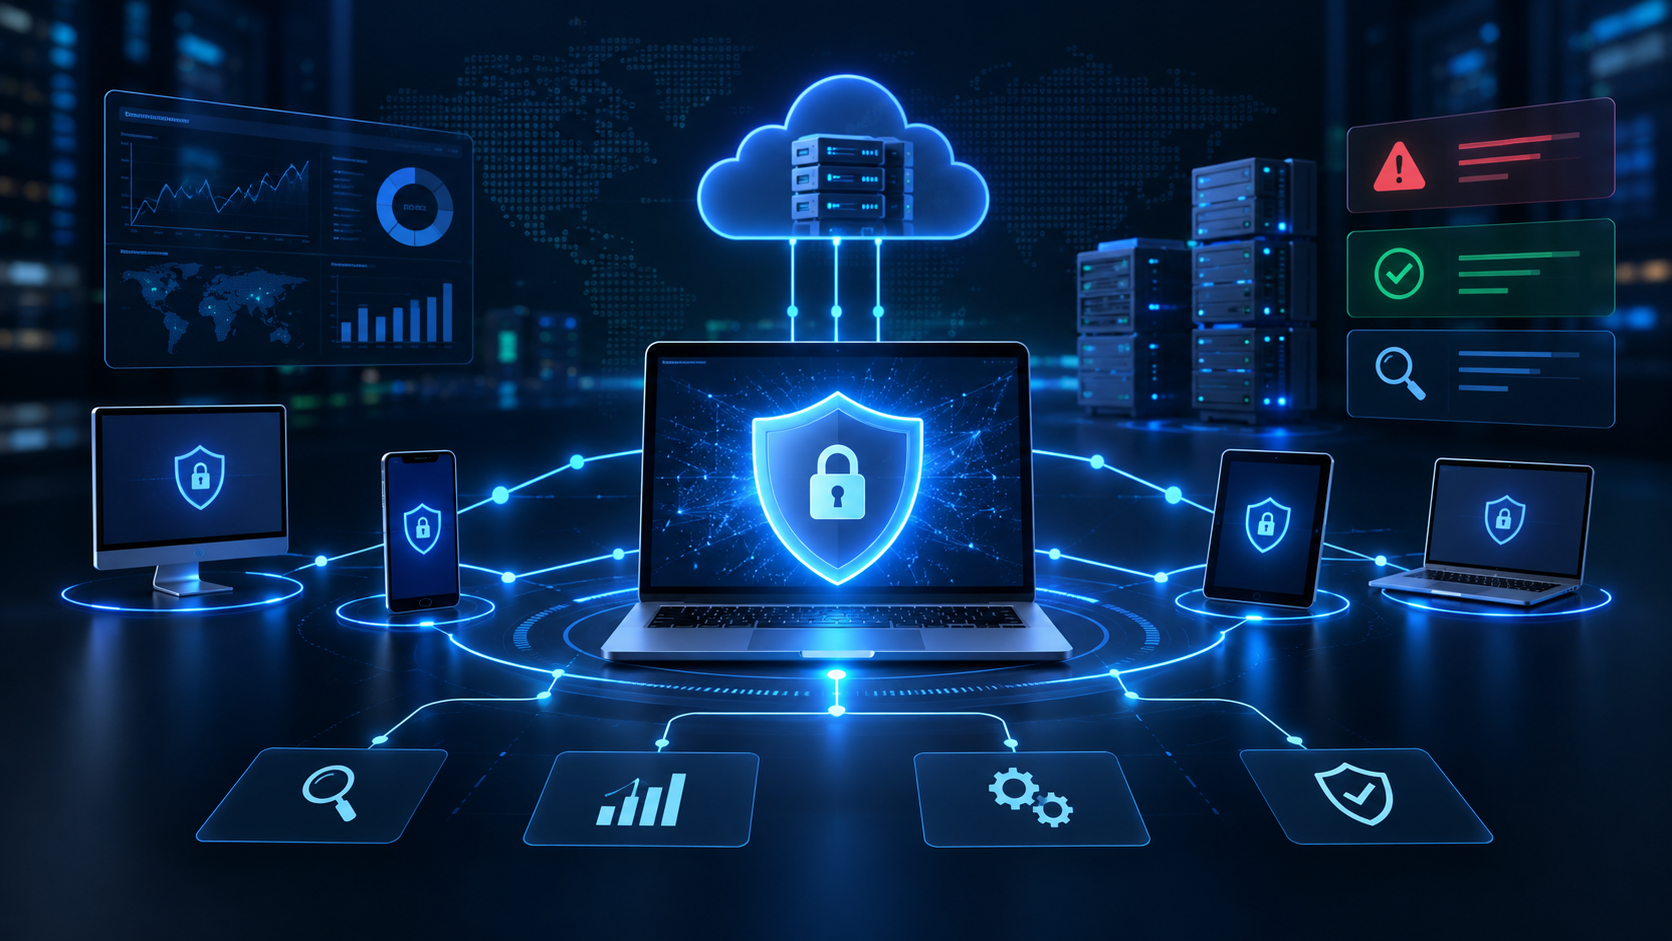
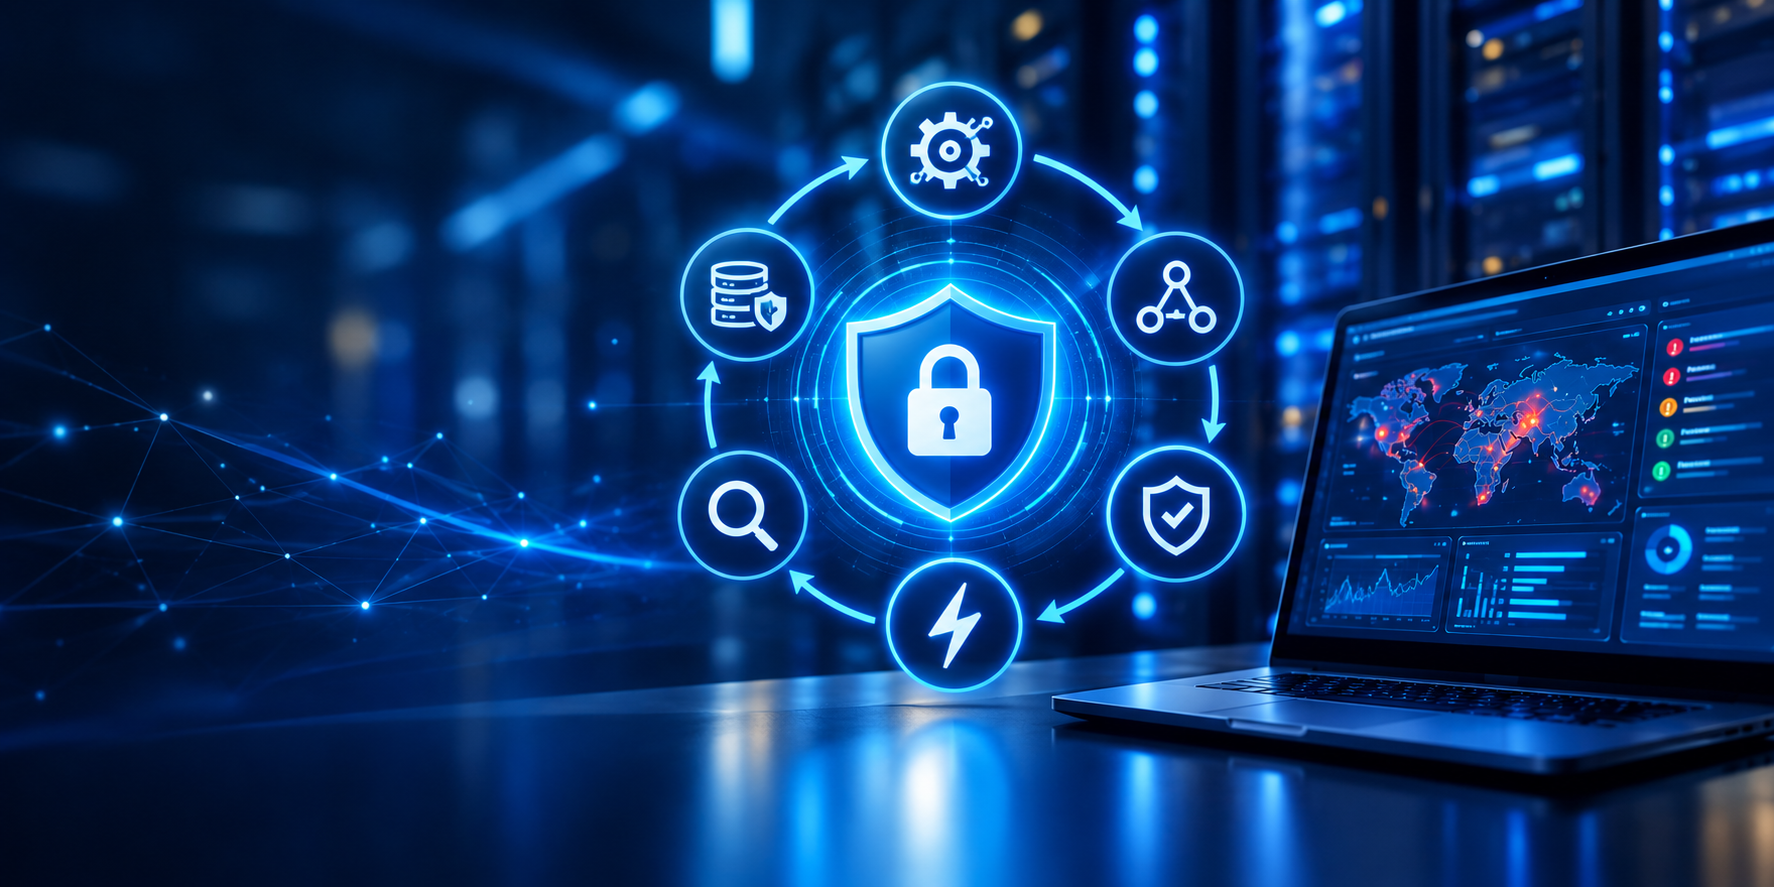
Protect your business with comprehensive Security Operations Center (SOC) Services designed to detect, analyze, and respond to cyber threats in real time. Our SOC team provides 24/7 monitoring, threat intelligence, incident response, vulnerability management, and security event analysis to safeguard your critical systems and data. By leveraging advanced security technologies and expert analysts, we help organizations strengthen their security posture, reduce risks, ensure compliance, and maintain business continuity in an increasingly complex threat landscape.

24/7 Security Monitoring

Continuous monitoring of your IT environment to detect and respond to threats in real time.

  • Real-time threat detection & alerting
  • Continuous log monitoring & analysis
  • Endpoint, network, and cloud security monitoring
  • Proactive incident identification

Threat Detection & Incident Response

Rapid detection, investigation, and containment of cyber threats.

  • Security incident investigation & triage
  • Malware, ransomware, and phishing detection
  • Incident response & remediation support
  • Root cause analysis and reporting

SIEM Implementation & Management

Centralized visibility and correlation across your security infrastructure.

  • SIEM deployment & configuration
  • Log aggregation & event correlation
  • Custom use cases and alert tuning
  • Compliance-focused reporting and dashboards

Threat Intelligence

Identify emerging threats before they impact your business.

  • Threat intelligence integration
  • IOC (Indicators of Compromise) monitoring
  • Dark web & threat landscape monitoring
  • Advanced threat hunting services

Endpoint Detection & Response (EDR/XDR)

Advanced protection for endpoints, users, and workloads.

  • Endpoint monitoring & behavioral analytics
  • XDR integration across cloud and endpoints
  • Endpoint investigation

Vulnerability Management

Identify and remediate security weaknesses proactively.

  • Vulnerability scanning & assessment
  • Patch management recommendations
  • Risk prioritization & remediation tracking
  • Internal and external asset scanning

Cloud Security Monitoring

Secure multi-cloud and hybrid environments with continuous oversight.

  • AWS, Azure, GCP & OCI security monitoring
  • Cloud posture management (CSPM)
  • Identity & access monitoring

Identity & Access Security

Protect user identities and privileged access.

  • MFA implementation & monitoring
  • AES 256 Encryption System
  • Privileged Access Management (PAM)
  • Role Based Access Control (RBAC)
  • Identity threat detection
  • User activity monitoring & anomaly detection

Compliance & Governance

Meet regulatory and security compliance requirements with confidence.

  • Compliance monitoring & reporting
  • Audit log management
  • Security policy enforcement
  • Support for ISO 27001, GDPR, HIPAA, PCI-DSS, SOC 2, RBI, IRDAI, NIST 800 53

Security Automation & SOAR

Accelerate response times through intelligent automation.

  • Automated incident response workflows
  • Security orchestration
  • Alert enrichment & ticketing integration
  • Reduced Mean Time to Detect (MTTD) & Respond (MTTR)

Reporting & Analytics

Actionable security insights for informed decision-making.

  • Executive security dashboards
  • Incident & risk reporting
  • Threat trend analysis

Managed SOC Services

End-to-end managed security operations tailored to your business.

  • Dedicated SOC analysts & security experts
  • 24/7 incident response support
  • Continuous security optimization
  • Managed detection and response (MDR) services
Enquire Now