Lumatrix

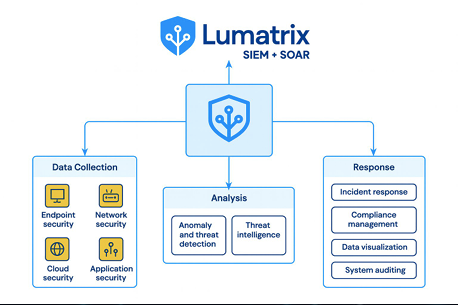
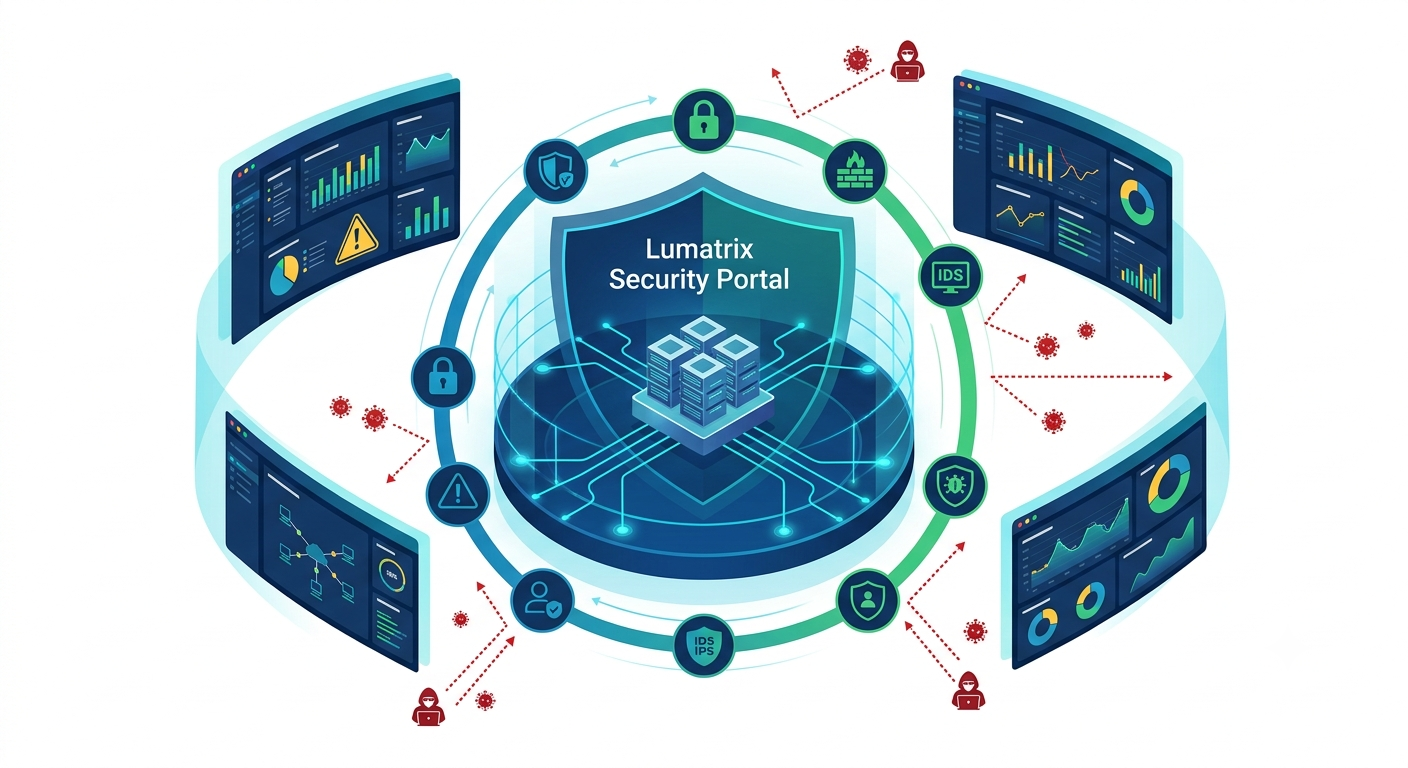
Lumatrix is an enterprise-grade Security Information and Event Management (SIEM) and Security Orchestration, Automation and Response (SOAR) platform. It delivers threat detection, compliance, and automated response across environments.​

View Workflow

Features of Lumatrix

  • LogCollection and Centralized Analysis​
  • ThreatDetection & Intrusion Monitoring​
  • Vulnerability and Risk Management​
  • Compliance and Audit Frameworks​
  • FileIntegrity Monitoring (FIM)​
  • SOARCapabilities​

Components of Lumatrix

Lumatrix is an advanced Security Operations solution, seamlessly integrating the power of Wazuh for SIEM, Shuffle Workflow for SOAR automation, and MISP for threat intelligence sharing. Built with a modular and scalable architecture, Lumatrix enables organizations to monitor, detect, analyze, and respond to security incidents in real time.

What makes Lumatrix unique is the deep customization delivered by Postiefs security experts, who fine-tune every deployment to align with each client’s specific infrastructure, compliance requirements, and business objectives. From automated playbooks for faster incident response, to tailored dashboards and enriched threat intelligence, Lumatrix ensures that security operations are not only robust but also highly adaptive.

With Lumatrix, enterprises gain a unified security ecosystem that reduces manual overhead, accelerates detection and response, and delivers actionable insights — all while staying flexible enough to grow with evolving security challenges.

Architecture of Lumatrix

  • Lumatrix Agents: Collect telemetry & logs from endpoints​
  • Lumatrix Manager: Core processing engine for alerts & correlation​
  • Lumatrix Data Lake: High-performance storage(Elastic/OpenSearch)​
  • Lumatrix Dashboard: Real-time monitoring, reporting & playbooks​

Why Lumatrix

  • Unified SIEM + SOAR (not just monitoring,but automated response)​
  • Cloud-native ready (AWS, Azure, OCI, On-prem)​
  • Custom dashboards & playbooks for enterprise use cases​
  • Cost-effective alternative to Splunk, Sentinal, QRadar